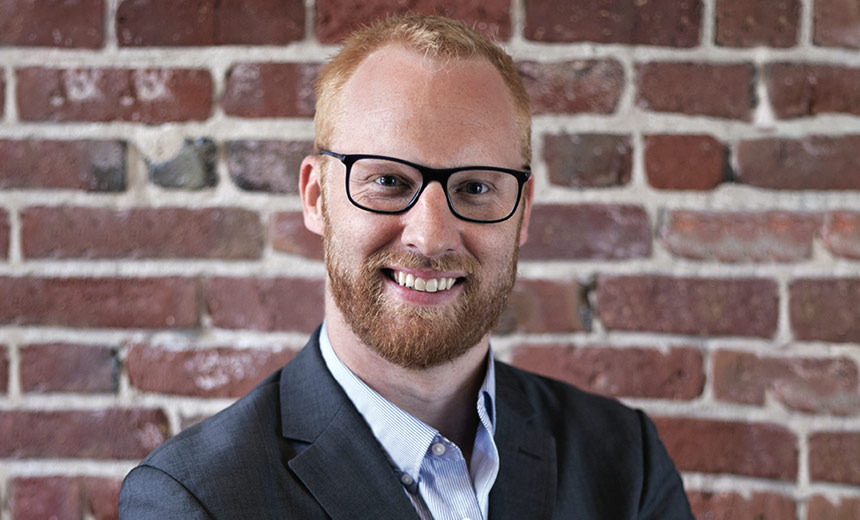
Casey Ellis, on the record.
1,435 items across 6 categories: press, broadcast, stage, and paperwork. Captured, displayed, and archived for posterity.
Healthcare breaches and data exposures. Is compliance with privacy regulations motivated by fear of fines?
CyberWire's Privacy Briefing newsletter from June 2021 examines healthcare data breaches and whether compliance with privacy regulations is driven primarily by fear of financial penalties. Casey Ellis provides analysis on the motivations behind organizational privacy practices and regulatory compliance in the healthcare sector.
Georgia Fertility Clinic Hit by Ransomware: Expert Commentary
Solutions Review published expert commentary on a ransomware attack affecting a Georgia fertility clinic. Ellis discussed the incident's implications for healthcare cybersecurity and the vulnerabilities that made the clinic a target for attackers.
Businesses must bank on secure future
An opinion piece in the Australian Financial Review argues that Australian businesses must prioritize cybersecurity in an increasingly hostile digital environment. Casey Ellis calls for organizations to embed security into their operational strategy rather than treating it as an afterthought to achieve long-term resilience.
Supreme Court Decision on Van Buren Case Restricts Excesses of CFAA, Is a Boon for Cybersecurity Research
CPO Magazine published an analysis of the U.S. Supreme Court's Van Buren v. United States decision, which narrowed the Computer Fraud and Abuse Act's scope. Casey Ellis is cited for his perspective on how the ruling benefits security researchers by providing clearer legal boundaries for vulnerability research and disclosure.
Which way now? U.S. narrows the scope of computer fraud legislation
Digital Journal published an analysis of the U.S. Supreme Court's decision narrowing the scope of the Computer Fraud and Abuse Act. Casey Ellis discusses the implications of the ruling for security researchers and the broader cybersecurity landscape.
Hackers are Heroes
App Sec Stats Flash podcast segment from May 2021 addresses the role of ethical hackers in cybersecurity. Casey Ellis argues that ethical hackers serve as essential defenders rather than criminals, emphasizing their positive contribution to strengthening security systems.
Vulnerability detection in IT assets by utilizing crowdsourcing techniques
U.S. Patent 11,019,091 outlines systems and methods for detecting vulnerabilities in IT assets through crowdsourced analysis of security data and feature vectors. The patent, filed by Casey Ellis, describes how similarity measurements between target systems and a corpus of known vulnerabilities enable community experts to identify previously unknown security weaknesses.
A Q&A with Crowdsourcing Cybersecurity Firm Bugcrowd’s Founder and Chairman, Casey Ellis
Crowd Sourcing Week published a Q&A interview with Casey Ellis, founder and chairman of Bugcrowd, in May 2021. Ellis discusses the crowdsourced security model and explains how the bug bounty industry addresses vulnerability discovery and remediation at scale.
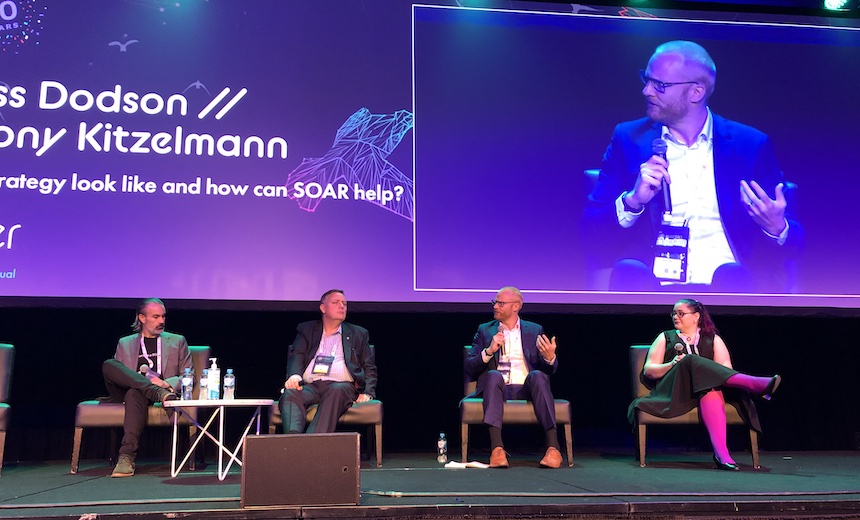
Taking on SOAR: The Challenges and Opportunities
A Bank Info Security article from May 2021 examines the challenges and opportunities of implementing Security Orchestration, Automation and Response technologies in organizations. Casey Ellis discusses how SOAR deployment requires careful planning and addresses both the technical and operational barriers that security teams encounter during implementation.
Speed Debating Panel
Opening Keynote Panel
Inside The Unlikely Romance: Crowdsourced Security from a Financial Services Perspective
Keynote: Release The Hounds, Part 2: 8 Years Is A Long Ass Time
The Economics of Software Flaw Discoveries, Exploits
An interview published in Bank Info Security examines the evolving landscape of software vulnerabilities and how organizations adapt their security strategies. Ellis discusses the changing dynamics around software flaw discoveries and exploits, addressing shifts in how enterprises approach vulnerability management.

How might we build a new internet?
iT Wire published "How might we build a new internet?" in April 2021, exploring theoretical and practical challenges of designing a more secure and resilient internet infrastructure. Casey Ellis contributes perspectives on the foundational security and resilience requirements necessary for internet redesign efforts.
When vulnerability disclosure goes sour: New GitHub repo details legal threats and risks faced by ethical hackers
The Daily Swig published an article examining a GitHub repository that documents legal threats faced by ethical hackers during vulnerability disclosure processes. Casey Ellis is cited as a contributor to the repository, which catalogs cases where security researchers encountered legal action despite following responsible disclosure practices.
Security Research and Disclosure: The Unauthorized Biography | Casey John Ellis | Nullcon March 2021
A Nullcon stage presentation from March 2021 titled "Security Research and Disclosure: The Unauthorized Biography" features Casey Ellis discussing the evolution of security research and market dynamics. Ellis covers how bug hunters can identify and capitalize on valuable research opportunities within the current threat landscape.
16 Strategies To Prevent Your Team Members From Adopting ‘Shadow IT’
Forbes published this Technology Council article, titled 16 Strategies To Prevent Your Team Members From Adopting Shadow IT, in April 2021. Casey Ellis of Bugcrowd advocates defining what violations look like, how to detect and prioritize them, and how to respond, calling it a low-cost process that reflects reduced IT control.
Vulnerability detection in IT assets by utilizing crowdsourcing techniques
U.S. Patent 10,972,494, filed in 2021, covers systems and methods for detecting vulnerabilities in IT assets through crowdsourced analysis of security attributes and attack surface comparisons. The patent, which lists Casey Ellis as an inventor, describes using feature vectors and community expert review to identify unknown vulnerabilities in target systems based on similarity measures within a corpus of known vulnerable assets.
Hackers And Cyber Criminals ARE NOT The Same
ITSPmagazine podcast episode from March 2021 examines the distinction between ethical hackers and malicious cybercriminals. Ellis discusses how non-profit organizations and community groups support legitimate hacking practices that benefit society by enabling security research and vulnerability disclosure.
Introduction to Disclose.io and the Current State of Hacker Safety
Panel Discussion
Plaintext Podcast Ep. 5 Featuring Bugcrowd Founder Casey Ellis
Duo Security's Plaintext podcast episode five features an interview with Bugcrowd founder Casey Ellis. Ellis discusses the history and evolution of bug bounty programs, the maturation of the industry, and his vision for the future of crowdsourced security.

Ryuk ransomware hits Spanish Government (Includes interview)
Digital Journal published this March 2021 article reporting that the Ryuk ransomware gang crippled Spain's State Public Employment Service (SEPE). Casey Ellis, Bugcrowd co-founder, says the incident shows common vulnerabilities exist in organizations of every size and that governments need to acknowledge the scale of threats they face.
Inside The Mind Of A Hacker Report | Unique Histories, Shared Destiny
ITSPmagazine published a feature examining findings from Bugcrowd's 2020 Inside the Mind of a Hacker report. Ellis provided context on demographic data, motivations, and specializations across the global ethical hacker community revealed in the research.
Keynote: Release The Hounds, Part 2: 8 Years Is A Long Ass Time
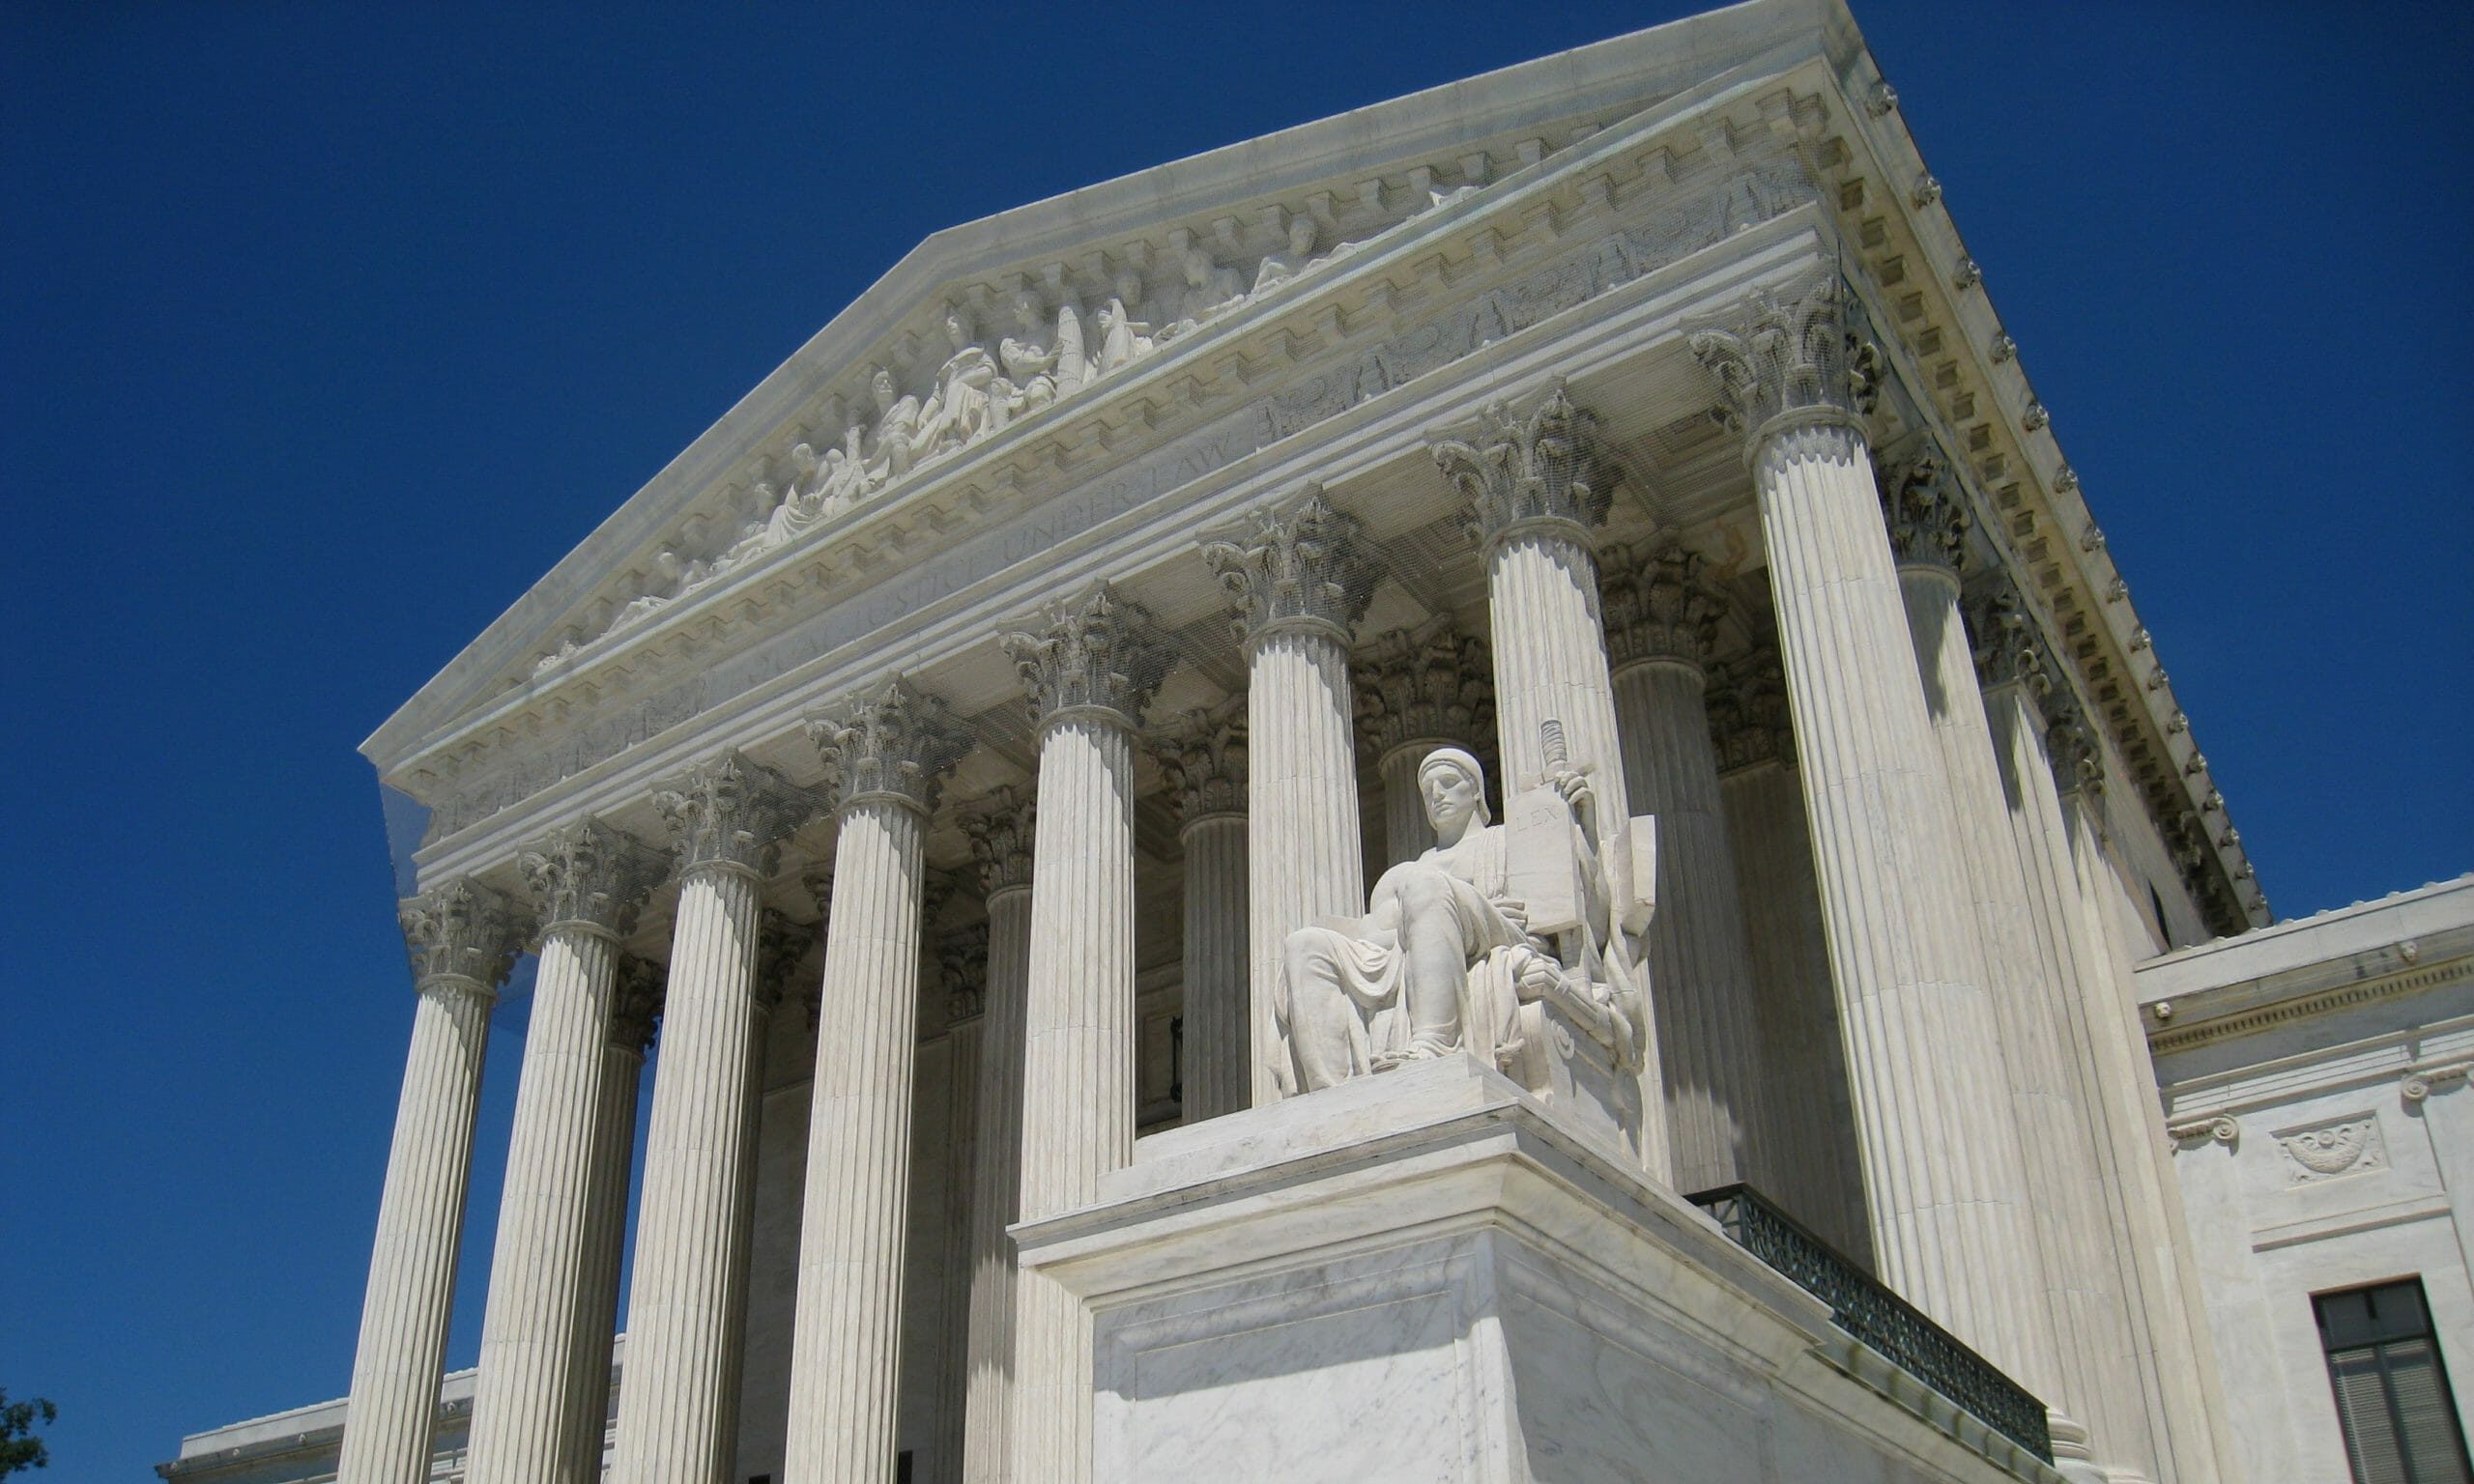
Supreme Court narrows interpretation of CFAA, to the relief of ethical hackers
The Supreme Court's decision to narrow the Computer Fraud and Abuse Act was covered by SC Magazine in March 2021. Casey Ellis was cited as welcoming the ruling for its potential to protect security researchers and ethical hackers from overly broad legal interpretations.
Supreme Court Votes to Limit Computer Fraud and Abuse Act
Bank Info Security reported on the U.S. Supreme Court's decision in Van Buren v. United States, which narrowed the scope of the Computer Fraud and Abuse Act. Casey Ellis commented on the ruling's implications for security researchers and the vulnerability disclosure landscape.
2020 Inside The Mind Of A Hacker Report | There Will Always Be Hackers‚ AI, We Just Need More
A 2021 podcast episode from Bugcrowd features Casey Ellis discussing findings from the 2020 Hacker Report alongside other security professionals. Ellis addresses the growing demand for ethical hackers and examines how artificial intelligence may shape the future of cybersecurity.
Responsible Disclosure Programs with Katie Moussouris & Casey Ellis | 401 Access Denied Ep. 22
A February 2021 episode of Cybrary's 401 Access Denied podcast features Casey Ellis and Katie Moussouris discussing vulnerability disclosure programs. Ellis and Moussouris outline best practice steps for organizations to safely receive and act on vulnerability information through formal disclosure programs.