Casey Ellis, on the record.
1,435 items across 6 categories: press, broadcast, stage, and paperwork. Captured, displayed, and archived for posterity.
Serious Log4j Security Flaw: Race Underway to Discern Scope
This BankInfoSecurity article from December 2021 covers the Apache Log4j 2 zero-day flaw and how security teams are working to gauge its scope. Casey Ellis, CTO and founder of Bugcrowd, says he has seen the flaw exploited via a Wi-Fi SSID and calls its long tail extraordinary.
Chinese Researchers Discover EwDoor Botnet Affecting up to 100,000 AT&T VoIP Servers
CPO Magazine published a report on the discovery of EwDoor, a botnet targeting AT&T VoIP servers that potentially infected up to 100,000 devices, as identified by Chinese security researchers. Casey Ellis commented on the security implications and threat landscape revealed by the botnet's widespread reach and targeting of critical communications infrastructure.
How Do I Find My Servers With the Log4j Vulnerability?
Dark Reading published a technical guide on identifying servers vulnerable to the Log4j flaw. Casey Ellis contributed advice and methods to help system administrators detect the vulnerability across their infrastructure.
Bug-Bounty Programs Shift Focus to Most Critical Flaws
Dark Reading published an analysis on how bug bounty programs are evolving to prioritize critical vulnerabilities with higher payouts. Casey Ellis discusses the strategic shift toward incentivizing researchers to focus on the most impactful security flaws rather than volume-based submissions.
'Vaccine' against Log4Shell vulnerability has potential -- and limitations
A December 2021 VentureBeat article covers Cybereason's "vaccine" workaround for the Log4Shell flaw in Apache Log4j servers. Casey Ellis, founder and CTO of Bugcrowd, tells VentureBeat the fix appears effective, though he calls it a supplementary tool rather than a cure-all and notes it does not work before Log4j 2.10.

Apache Log4j Threatens, Well, Everything
This Security Boulevard article from December 11, 2021, covers the actively exploited Apache Log4j flaw, CVE-2021-44228, in the widely used Log4j2 Java logging library. Casey Ellis, founder and CTO at Bugcrowd, warns that the library's ubiquity and many exploit paths will complicate patching, and urges teams to immediately locate Log4j in their environments.
NVD: It’s Another Record Year for Vulnerabilities
This Infosecurity Magazine article, published December 9, 2021, reports that the National Vulnerability Database logged another record number of software vulnerabilities, marking the fifth consecutive year of such totals. Casey Ellis, CTO at Bugcrowd, says the record reflects the pace of technological development, since more software produced means more vulnerabilities exist.
2021 marks another record year for security vulnerabilities
TechRepublic published an article examining the record number of security vulnerabilities disclosed in 2021. Casey Ellis provides insight into the factors driving the surge in vulnerability disclosures and their implications for the security industry.
With 18,378 vulnerabilities reported in 2021, NIST records fifth straight year of record numbers
ZDNet published a report on NIST data showing that 2021 saw 18,378 vulnerabilities discovered, continuing a fifth consecutive year of record numbers. Casey Ellis commented on the vulnerability landscape and the implications of sustained increases in reported security flaws.
How to get started with bug bounties and finding vulnerabilities | Cyber Work Podcast
A Cyberwire podcast episode from December 2021 features Casey Ellis discussing how to begin participation in bug bounty programs and the process of identifying vulnerabilities. Ellis provides guidance on entry points for security researchers interested in coordinated vulnerability disclosure and bug bounty participation.
AT&T Looks to Shut Down Botnet that Attacked 5,700 Network Appliances
eSecurity Planet reported on AT&T's efforts to shut down the EwDoor botnet, which compromised over 5,700 carrier-grade network address translation devices. Casey Ellis commented on the incident's significance for critical infrastructure security and the importance of coordinated response efforts against emerging botnet threats.
Arrest Points to Ubiquiti Breach Being an Inside Job
BankInfoSecurity reported on the arrest of a former Ubiquiti employee charged with orchestrating a data breach and extortion attempt against the networking company. Casey Ellis commented on the incident's implications for corporate security practices and insider threat detection.
Searching for Bugs in Open Source Code
Security Boulevard published an article on the challenges and importance of proactively identifying and fixing security vulnerabilities in open-source software. Casey Ellis discusses the need for systematic approaches to vulnerability discovery and remediation in open-source projects.
300,000 banking Trojan infections from Google Play in 4 months
Security Magazine reported on a wave of banking trojan infections from malicious apps on Google Play that resulted in over 300,000 infections across four months. Casey Ellis contributed analysis on the threat landscape and the security implications of malware distribution through official app marketplaces.
CTO Talk: Q&A with Bugcrowd’s Casey Ellis
Verdict published a Q&A interview with Casey Ellis, founder and CTO of Bugcrowd, in November 2021. Ellis discusses how cybersecurity has evolved and explains the role crowdsourced security plays in modern defense strategies.
Q&A: Casey Ellis
A Q&A session published by Duo Security explores Casey Ellis's perspectives on bug bounties and vulnerability disclosure practices. Ellis discusses the evolution of bug bounty programs and shares insights on the future direction of how organizations discover and address security vulnerabilities.
Decipher Podcast: Casey Ellis
Decipher Security Podcast published an episode featuring Casey Ellis on November 23, 2021. Ellis discusses how vulnerability disclosure programs have evolved, gained adoption, and become standardized in the United States and internationally.
Malicious Golang program attacks e-commerce servers
A report from SC Magazine details malicious Golang malware targeting e-commerce servers to steal payment information. Casey Ellis provided analysis on the threat's implications for retail infrastructure and payment security vulnerabilities.
Digital Bounty Hunters Want To Help Businesses Track Down
A Forbes article examines the emerging practice of applying bug bounty models to identify bias and discrimination in artificial intelligence systems. Casey Ellis discusses how crowdsourced security approaches can be adapted to surface algorithmic fairness issues before they cause harm to users and organizations.

Ethical Hackers Prevented $27B in Cybercrime
The Security Boulevard article "Ethical Hackers Prevented $27B in Cybercrime," published November 17, 2021, examines how security researchers skew younger, are more entrepreneurial, and span generations. Casey Ellis, founder and CTO of Bugcrowd, comments that 79% of ethical hackers taught themselves using online resources and calls the cohort's impact on thwarting cyberattacks monumental.
U.S. Government Details Federal Agency Incident Response
Duo Security published an analysis of new U.S. government directives establishing incident response requirements for federal civilian agencies. Casey Ellis is quoted discussing the practical implications of the government's clearer cybersecurity incident playbooks and their effect on federal agency preparedness.
Ethical Hackers Stymie $27bn of Cybercrime
A report in InfoSecurity Magazine details research estimating that ethical hackers prevented over $27 billion in cybercrime damages during a one-year period. Casey Ellis contributed to the research, which quantifies the financial impact of vulnerability disclosure and coordinated security research on reducing criminal losses.
Midsize Companies Still Struggle with Security
This Security Boulevard article from November 2021, titled "Midsize Companies Still Struggle with Security," examines cybersecurity challenges facing midsize organizations. Casey Ellis, founder and CTO of Bugcrowd, says the main midmarket weaknesses are attack surface drift, patch management, and application security, and suggests vulnerability disclosure programs to address them.
How Hackers are Defending Control Room Networks
Bug Bounty or Beg Bounty?
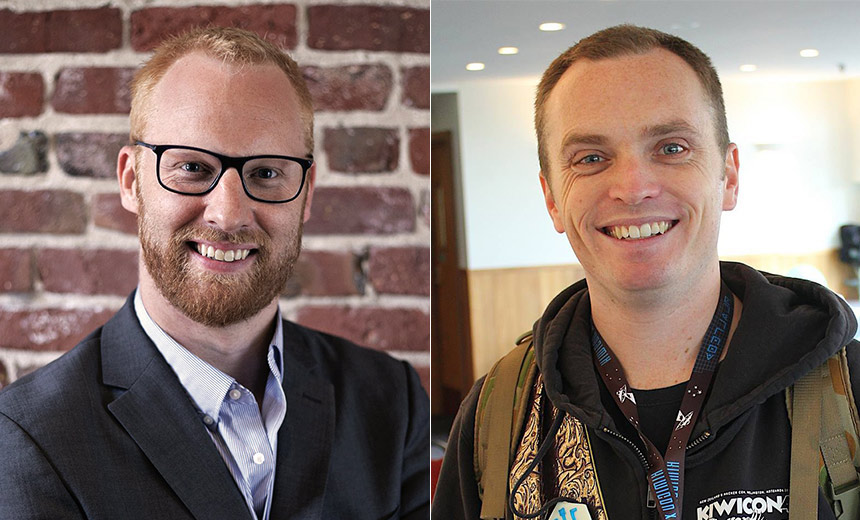
Why Reporting Security Bugs Can Be Fraught With Tension
This 2021 video interview from BankInfoSecurity examines the tensions researchers face when reporting vulnerabilities to organizations without disclosure policies. Casey Ellis, founder, CTO and chairman of Bugcrowd, says legal protections are needed for responsible researchers, who function as the internet's immune system, and he is involved with Disclose.io, a safe harbor initiative.
Patching Process Remains a Security Bottleneck
This October 2021 Security Boulevard article, Patching Process Remains a Security Bottleneck, covers why patching stays slow and complex. Casey Ellis, founder and CTO of Bugcrowd, calls patch management one of the unavoidable chores of IT management and says failures usually stem from incomplete asset inventories.
Cyber-security threat hunters seek legal protections
Published by The Register on October 11, 2021, this article reports on efforts by the Cybersecurity Advisors Network to secure legal protections for cyber-security threat hunters. Casey Ellis, founder, chair, and CTO of Bugcrowd, is among the figures who endorse the network's efforts, alongside Katie Moussouris and Ciaran Martin.

Cybersecurity is a Team Sport
Recorded: Thursday 7 October 2021 @ 10:00am AEDT • Online You’re not alone in the fight to protect your organisation from cyber threats. Unfortunately, neither are your attackers. So, where does that leave you? Circle Leader: Michael Loewy, Tide Foundation Contributors: Dr Stephenie Andal, Cyber Security CRC; Tony Aramze, RMIT; Casey Ellis, Bugcrowd; Peter Soulsby, NTT Ltd ---------------------------------------- Tech23 Impact Circles ---------------------------------------- Tech23's Impact Circles are an interactive opportunity for curious minds from across Australia and beyond to come together around the big opportunities Australia has to create new industries, smarter solutions, and a better world. https://tech23.com.au/2021/circles/ ---------------------------------------- Zoom meetings were moderated by Rachel Slattery, Director of Slatterys; and Adina Thavisin, Captain of Content and Community, Tech23.
Cybersecurity Awareness Month with Casey Ellis, CTO, Bugcrowd and Beau Woods, Senior Advisor, CISA
The CyberWire published a video segment featuring Casey Ellis, CTO of Bugcrowd, and Beau Woods, Senior Advisor at CISA, discussing cybersecurity awareness during October 2021. Ellis and Woods explored implications of recent security incidents for security leaders and organizational defense strategies.