Casey Ellis, on the record.
1,435 items across 6 categories: press, broadcast, stage, and paperwork. Captured, displayed, and archived for posterity.
Election Result Websites Have Capacity to Create 'Noise'
Statescoop published an article examining how election result websites could be manipulated to spread false information. Casey Ellis comments on security vulnerabilities in these systems and their potential to create confusion and undermine public trust during elections.
Mythbusting the 'grey zone': The evolution of vulnerability disclosure
Trump signs law that makes hacking election systems a federal crime
The Washington Examiner reported on President Trump signing legislation that elevates hacking election systems to a federal crime. Casey Ellis commented on how the law affects security researchers and adversaries seeking to access election infrastructure.
Whole Kids smashes $500,000 equity crowdfunding goal, securing the likes of Kate Morris and Casey Ellis as backers
Smart Company reported that Whole Kids exceeded its $500,000 equity crowdfunding target, with backers including Kate Morris and Casey Ellis. Ellis joined the funding round as an investor supporting the startup's growth in the nutrition and children's health sector.
How the Pandemic is Reshaping the Bug-Bounty Landscape
ThreatPost published an article examining how the COVID-19 pandemic and remote work shift have reshaped the bug bounty landscape. Casey Ellis provides analysis on the pandemic's effects on corporate attack surfaces and vulnerability disclosure practices.
HOW TO START in BUG BOUNTY IN 2020 with Casey Ellis, BugCrowd
Cloud Security Podcast featured Casey Ellis from BugCrowd discussing how to launch a career in bug bounty hunting in 2020. Ellis provided foundational guidance and a roadmap for aspiring security researchers entering the field.
How ethical hackers are trying to protect the 2020 U.S. elections
VentureBeat published an article examining how ethical hackers are working to identify and remediate vulnerabilities in U.S. election infrastructure before the 2020 presidential vote. Casey Ellis discusses the ethical hacking community's role in discovering security gaps and supporting efforts to strengthen election systems.

Time for a Change: Why It's More Important Than Ever to Revisit the CFAA
Training Dates - November 2-4, 2026 / Conference Dates - November 5-6, 2026It's our 25th Anniversary year!Get ready for an unforgettable experience at the OWASP Global AppSec USA Conference!*Training and Conference attendance are eligible to receive CPE CreditsFrom November 5–6, 2026, connect with over 800 hundred security experts, thought leaders, and practitioners. Be a part of something extraordinary at the OWASP Global AppSec US Conference, OWASP's largest US Conference, taki...
How security researchers should view the Voting Systems Act
Digital Journal published Casey Ellis's commentary on the proposed Voting Systems Act and its implications for security researchers in October 2020. Ellis examined both the potential benefits and drawbacks the legislation could create for researchers studying voting system vulnerabilities.
How security researchers should view the Voting Systems Act
Digital Journal published Casey Ellis's commentary on the DEFEND the Voting Systems Act in October 2020, examining its implications for security research. Ellis discussed how the legislation could affect good-faith vulnerability disclosure and the security research community's ability to strengthen voting systems.
Australian Cyber Week 2020
OzCyber Unlocked podcast featured Casey Ellis discussing Australian Cyber Week 2020 and its significance to the cybersecurity landscape. Ellis explored key topics shaping Australia's cybersecurity priorities and community engagement during the event.
Defending U.S. Voting Processes Now and into the Future
This Infosecurity Magazine blog post from October 14, 2020, is titled Defending U.S. Voting Processes Now and into the Future. Written by Casey Ellis, Founder and CTO of Bugcrowd, it examines security pressures on the 2020 U.S. election, including first-time digital voters and growing reliance on connected voting systems.
Microsoft leads effort to disrupt infamous TrickBot botnet
Silicon Angle reported on Microsoft's coordinated takedown effort against the TrickBot botnet infrastructure in October 2020. Casey Ellis contributed analysis on the significance of the disruption operation and its implications for combating large-scale botnet threats.
Keynote: The Unlikely Romance, Part 2: What Now?
ROOTCON is the Philippines' longest-running hacker conference.

Voting machines pose more problems in US elections than outside actors
ITWire published an article examining threats to US election integrity. Casey Ellis is quoted arguing that vulnerabilities in voting machine hardware and software present a greater risk to elections than external cyberattacks.
16 Software Development Trends That Will Soon Dominate The Tech Industry
Forbes published a panel piece on sixteen software development trends expected to shape the tech industry. Casey Ellis contributed a prediction on a key trend poised to dominate software development practices.
Bug Bounty FAQ: Top Questions, Expert Answers
Threatpost published a bug bounty FAQ feature in September 2020 addressing common questions about bug bounty programs. Ellis provides answers on how these programs function, their value to organizations, and implementation best practices.
Uber exec covered-up ransom payment for millions of drivers (Includes interview)
This 2020 Digital Journal article reports that Uber paid hackers a ransom after they downloaded a database of personal data, and that the payment went undisclosed. Casey Ellis, founder of Bugcrowd, says the affair has shaped public views of hackers and that ethical researchers must be distinguished from bad actors.
Legality of Security Research to be Decided in US Supreme Court Case
Dark Reading published an article on a Supreme Court case examining the legality of security research under the Computer Fraud and Abuse Act. Casey Ellis provided commentary on the Van Buren v. United States case and its implications for how the CFAA applies to security researchers.
Online voting vendor Voatz urges Supreme Court to limit security research
Ars Technica reported on online voting vendor Voatz's effort to use the Computer Fraud and Abuse Act to restrict security research into its platform. Casey Ellis opposed the move, arguing that such legal tactics undermine good-faith security research necessary to identify vulnerabilities in critical voting systems.
Legality of Security Research to be Decided in US Supreme Court Case
Dark Reading published coverage of a US Supreme Court case examining the legality of security research under the Computer Fraud and Abuse Act. Casey Ellis provided expert commentary on the case's implications for security researchers and the interpretation of CFAA provisions.
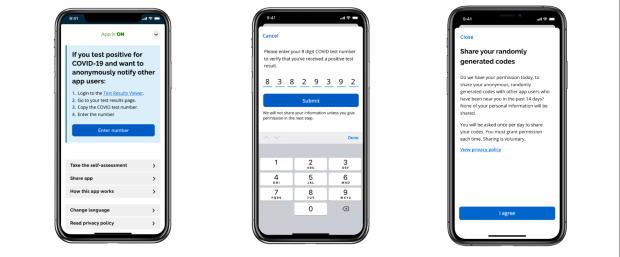
Vulnerability disclosure program needed to ensure confidence in COVID apps, says expert
IT World Canada published Casey Ellis's commentary on COVID-19 contact tracing apps in September 2020. Ellis argues that government contact tracing apps require formal vulnerability disclosure programs to build public trust and maintain security standards.
被“白帽黑客”吐槽,漏洞赏金被质疑是“作秀”
Fortune China published an article examining criticism from security researchers about bug bounty programs and whether they function as genuine security initiatives or public relations exercises. The piece discusses concerns raised by white-hat hackers, including perspectives on the effectiveness and transparency of vulnerability reward platforms in the security industry.
Facebook to warn third-party developers of vulnerable code
TechCrunch published a story on Facebook's plan to alert third-party developers about vulnerable code in their applications. Casey Ellis commented on the initiative, noting its significance for improving security awareness across the developer ecosystem.
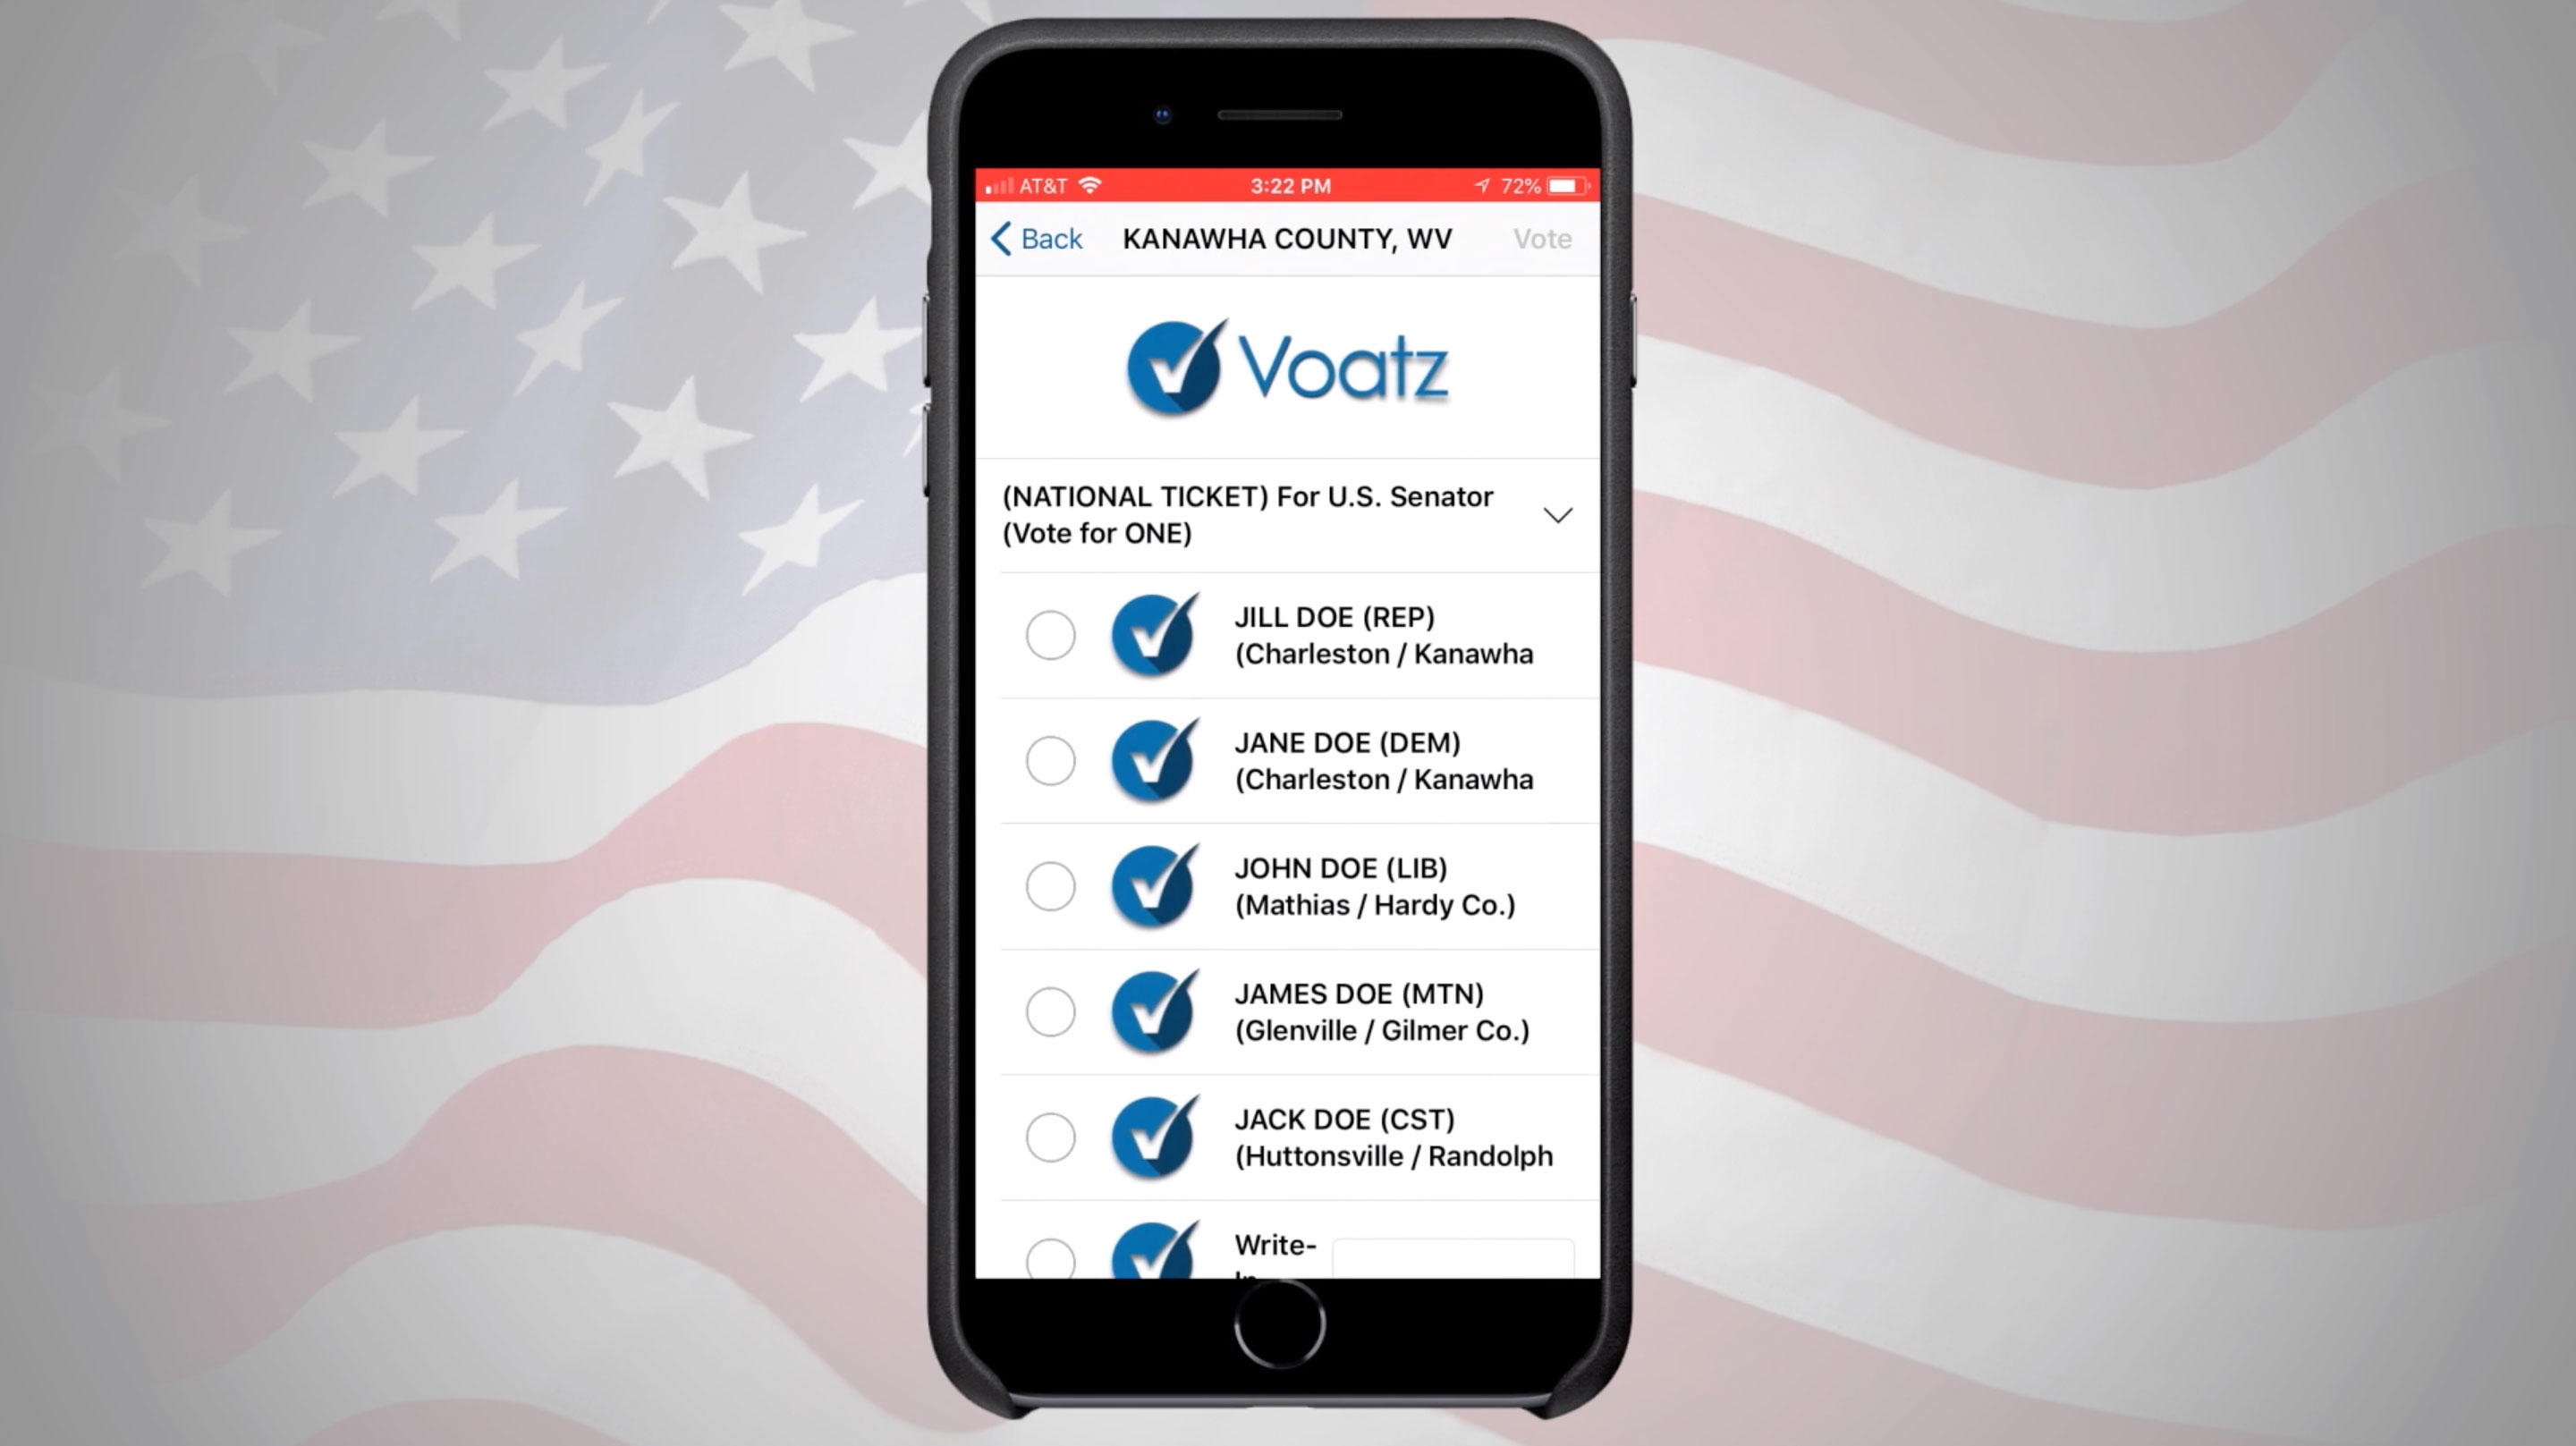
Online-voting company pushes to make it harder for researchers to find security flaws - CNET
This CNET news article from September 3, 2020 reports on e-voting company Voatz urging the Supreme Court to limit security research to authorized testing. Casey Ellis, founder of Bugcrowd, is quoted saying that making unauthorized access illegal would leave researchers unable to do their jobs while malicious hackers ignore the law.

If you were 'king,' how would you defeat ransomware?
ITWire published a feature in which Casey Ellis outlines a strategic approach to combating the global ransomware problem. Ellis describes the multifaceted solutions he would implement if positioned to address ransomware at scale.
What's behind Apple's iOS security research device program?
Digital Journal published an article examining Apple's iOS security research device program and its implications for vulnerability discovery. Casey Ellis analyzes the motivations behind Apple's initiative to distribute specially-configured iPhones to security researchers and assesses the program's potential impact on device security.
What's behind Apple's iOS security research device program?
Digital Journal published an article examining Apple's iOS security research device program and its implications for vulnerability discovery. Casey Ellis analyzes the program's motivations and potential impact on the security research community's ability to identify weaknesses in Apple's platform.
Lessons from Uber: Be crystal clear on the law and your bug bounty policies
SC Magazine published an article examining legal lessons from Uber's security breach incident and the importance of transparent bug bounty program governance. Casey Ellis discusses how organizations must establish clear, legally compliant bug bounty policies to protect both researchers and the company from liability and misunderstandings.
Former Uber CSO Charged Over Alleged Breach Cover-Up
Infosecurity Magazine reported on charges filed against Uber's former Chief Security Officer over an alleged breach cover-up. Casey Ellis commented on the case's implications for the CISO role and the responsibility of security leaders in corporate governance.