Casey Ellis, on the record.
1,435 items across 6 categories: press, broadcast, stage, and paperwork. Captured, displayed, and archived for posterity.
Data Breach Cover-Up: Uber's Former CSO Faces up to 8 Years Behind Bars
Secure World Expo published an industry news item on federal charges against Uber's former Chief Security Officer for a data breach cover-up. Casey Ellis commented on the case and connected it to the broader evolution of vulnerability disclosure ethics and corporate accountability standards.

Five Essentials for Running a Successful Bug Bounty Program
This broadcast webinar, Five Essentials for Running a Successful Bug Bounty Program, is published by Threatpost and targets organizations launching bug bounty programs, CISOs, and white hat hackers. Casey Ellis, CTO and founder of Bugcrowd, is a panelist and member of the CTI League, a coalition combating cyberthreats that arose amid COVID-19.
FireEye’s bug bounty program goes public
SC Magazine reported on FireEye's decision to open its previously private bug bounty program to external security researchers. Casey Ellis contributed to the piece as a bug bounty program expert offering perspective on the company's shift toward broader vulnerability disclosure practices.
What a Biden-Harris White House Could Mean for Tech Policy
A Wall Street Journal article from August 2020 examines potential technology policy shifts under a Biden-Harris administration, addressing antitrust enforcement, data privacy regulation, and Section 230 reform. Casey Ellis contributes perspective on how these policy areas could reshape the technology sector's regulatory landscape.
Vulnerability Economics: Understanding the Real Value of Security Flaws in Software
Bugcrowd hosted a webinar in August 2020 on vulnerability economics and the business impact of security flaws in software. Casey Ellis presented a framework for understanding how organizations should value and prioritize the remediation of discovered vulnerabilities.
3.1M records tied to medical software company Adit found exposed online
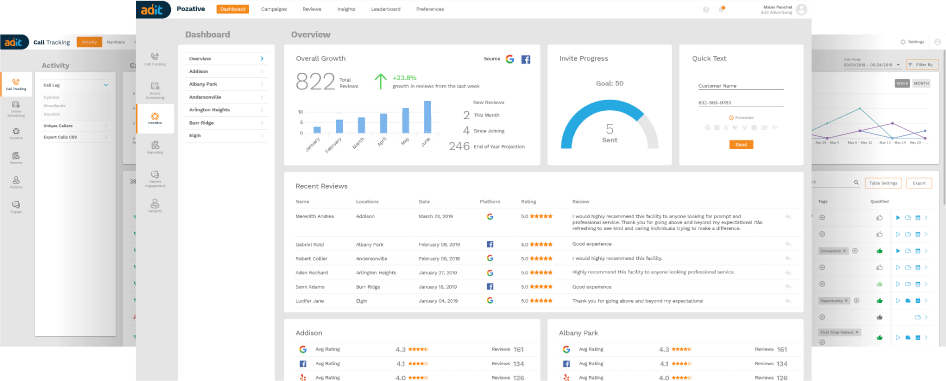
Silicon Angle reported on a data exposure incident affecting medical software company Adit, in which 3.1 million patient records were discovered unsecured online. Casey Ellis helped identify the exposure and coordinated its disclosure to the company and relevant authorities.

Hacking Democracy II: On Securing an Election Under Times of Uncertainty and Upheaval
Voting Village Speaker Track 2020 Virtual Q&A on Discord on the #vmhv-talks-questions-text channel All times Pacific Time (Schedule begins on Page 2) Google Calendar View Watch on YouTube:https://www.youtube.com/channel/UCnDevqsxt3sO8chqS5MGvwg Watch on Twitch: https://twitch.tv/votingvillag...

Medical Device Vulnerability Disclosure
The Biohacking Village at DEF CON: collaborating for cybersecurity safety and innovation in healthcare since 2014. Medical device security, CVD, labs & more.
Hackers and Defense Officials Unite Online at DEF CON 28
Clearance Jobs covered the virtual DEF CON 28 hacking conference, which brought together independent hackers and defense officials to strengthen national security practices. Casey Ellis participated in the event, contributing to discussions between the hacker community and government representatives on vulnerability disclosure and defensive security improvements.
Should privacy act terms of service violations be a crime?
Digital Journal published an article examining whether violations of website terms of service should be prosecuted as crimes under the Computer Fraud and Abuse Act. Casey Ellis contributed perspective to the legal debate surrounding enforcement of privacy obligations and the scope of computer fraud statutes.
Google Ditches Patch-Time Bug Disclosure in Favor of 90-Day Policy
Google Project Zero shifted its vulnerability disclosure policy away from patch-time requirements to a standardized 90-day deadline, according to Threatpost. Casey Ellis analyzed the implications of the policy change and its effects on the vulnerability disclosure landscape.
Casey John Ellis Interview
Hakluke published a video interview with Casey Ellis on July 31, 2020. Ellis discusses his career path as a developer, the influence of a book on his decision to work remotely, and how that shift enabled him to pursue additional interests.
Apple to send research phones to trusted hackers
Apple launched a Security Research Device Program providing specially configured iPhones to vetted security researchers, as reported by SC Magazine. Casey Ellis was among the trusted hackers selected to receive a research phone to identify iOS vulnerabilities.

How to Prioritize Cybersecurity for Your Startup
SAP's critical bug allows unrestricted access to ERP
Digital Journal published an article on a critical vulnerability in SAP's RECON software that could allow unauthenticated attackers unrestricted access to enterprise resource planning systems. Casey Ellis warned about the severity of the flaw and its potential impact on organizations relying on SAP infrastructure.
Critical SAP flaw puts 40,000 users at risk
SC Magazine published an article on a critical 10/10 severity vulnerability in an SAP application affecting approximately 40,000 customers. Casey Ellis commented on the risk and implications of the flaw for organizations using the affected SAP systems.
Cybersecurity: How Secure Are We?
Taking Stock Estimating Vulnerability Rediscovery
A Harvard Belfer Centre paper examines vulnerability rediscovery rates and collision dynamics in government disclosure processes. Casey Ellis contributes analysis on how security researchers and vendors encounter duplicate vulnerability reports, informing policy discussions around coordinated disclosure timelines and resource allocation.
Online: Cyber security: How secure are we?
Innovation Bay hosted an online panel discussion on cybersecurity challenges and the current state of digital security for individuals and organizations. Casey Ellis participated in the discussion, sharing perspective on security challenges facing the broader industry.
Human hackers will continue to beat AI for a decade
SC Magazine published an article in which Casey Ellis argues that human hackers will outperform artificial intelligence in offensive security tactics for approximately a decade. Ellis contends that human creativity and intuition provide advantages over AI systems in identifying and exploiting security vulnerabilities.
Study of global hackers and the economics of security research - Help Net Security
Help Net Security published this June 2020 article on a Bugcrowd study of global hackers and the economics of security research. Casey Ellis, CTO of Bugcrowd, comments that organizations made five times as many coordinated disclosures in the past year, which he links to the value of transparency and growing social responsibility.
Bugcrowd-Studie: Schutz kritischer Infrastruktur erfordert menschliche und künstliche Intelligenz
A Bugcrowd study published on OpenPR.de examines how protecting critical infrastructure requires combining human and artificial intelligence. Casey Ellis provides perspective on the importance of leveraging both human ingenuity and AI systems to strengthen security defenses against evolving threats.
AI alone isn't enough to thwart cyberattacks
A Betanews article examines the limits of artificial intelligence in cybersecurity defense. Casey Ellis argues that AI tools alone cannot match the creativity and adaptability of human attackers, and that effective defense requires combining automated systems with human expertise and ingenuity.
Neurodiversity on the rise among career hackers
Computer Weekly published an article examining the growing recognition of neurodiversity among ethical hackers and security professionals. Casey Ellis comments on how neurodivergent individuals bring distinct advantages to creative problem-solving and security research within the hacking community.
Bugcrowd Report Highlights Need for Blend of Human Ingenuity and AI-Powered Security Solutions to Protect Critical Infrastructure
A Bugcrowd report published by Business Wire examines the role of human expertise and artificial intelligence in protecting critical infrastructure. Casey Ellis emphasizes that effective security requires combining human ingenuity with AI-powered solutions rather than relying on either approach alone.
Bug bounty powerhouse: India takes top spot for Bugcrowd hackers worldwide
The Daily Swig reports on a Bugcrowd study showing India as the leading country for security researchers on the platform. Casey Ellis discusses the findings and India's emergence as a major hub for bug bounty hunters participating in coordinated vulnerability disclosure.
Coin Telegraph
Cointelegraph reported on an Israeli software firm's decision to pay a 250,000 dollar Bitcoin ransom following a ransomware attack. Casey Ellis commented on the difficult trade-offs companies face when deciding whether to pay ransom demands versus other response options.
16 Software Development Trends That Will Soon Dominate The Tech Industry
Forbes published a roundup of 16 software development trends expected to shape the tech industry, featuring input from members of its Technology Council. Casey Ellis contributed a prediction on a key trend poised to influence software development practices.
Terms of engagement: US computer crime laws out of step with changing attitudes to pen tests, ethical hacking
The Daily Swig published an article examining how US computer crime laws lag behind evolving practices in penetration testing and ethical hacking. Casey Ellis discusses how the Computer Fraud and Abuse Act creates legal uncertainty for security researchers conducting authorized testing in good faith.
Supply Chain Attacks: Securing Our Planes, Trains & Automobiles
A Bugcrowd webinar from June 2020 examines supply chain attacks and their impact on critical infrastructure sectors. Casey Ellis discusses how vulnerabilities in third-party components create security risks across transportation and related industries.